

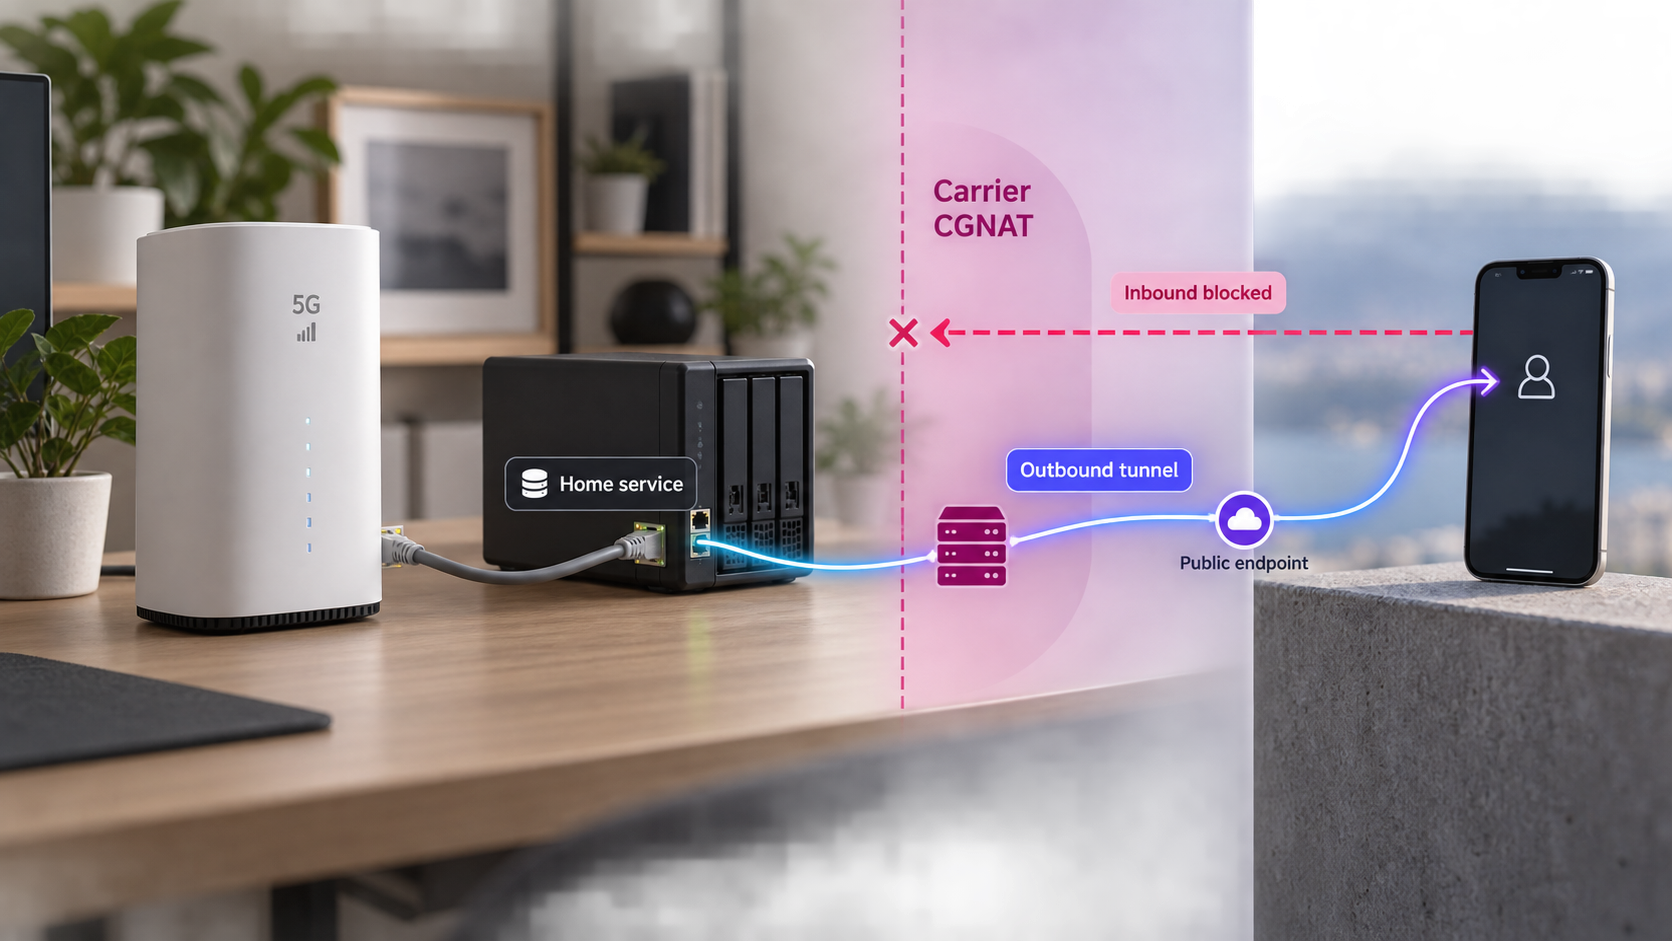
Diagnose the carrier NAT boundary, choose the right remote-access method, and verify it safely
T-Mobile Home Internet can use a different inbound-connectivity model from broadband services that assign a directly reachable public IPv4 address. When carrier-grade NAT is present, a forwarding rule on your home gateway cannot create the corresponding mapping inside the carrier network. This guide explains how to recognize that boundary, why common router workarounds fail, how to evaluate IPv6, and how to publish a selected service through an outbound Localtonet tunnel. It also covers local testing, protocol selection, remote verification, routine operation, security, and troubleshooting.
📋 What's in this guide
The short answer
Traditional IPv4 port forwarding generally cannot produce a publicly reachable port when a T-Mobile Home Internet connection is behind carrier-grade NAT, usually shortened to CGNAT. A rule on your home gateway controls only the translation performed by that gateway. It cannot create an inbound mapping on an upstream carrier gateway that you do not administer.
This limitation applies to unsolicited inbound IPv4 traffic. It does not mean ordinary internet access will stop working. Web browsing, streaming, cloud-managed devices, and many online games initiate outbound sessions and can operate through NAT. The problem appears when an outside user or system must initiate a connection to something inside your home, such as a self-hosted website, webhook receiver, game server, TCP application, UDP service, or file server.
There are several possible responses. You can ask the provider whether a publicly reachable address is available for your specific service, evaluate end-to-end IPv6, place the application on an external host, operate your own relay, use a private mesh VPN, or create an outbound managed tunnel. The correct choice depends on whether the service should be public or limited to authorized devices.
With Localtonet, our client runs on a device that can reach the local service and establishes an outbound connection to a Localtonet relay. The tunnel provides a public URL or public host and port. This workflow does not require inbound router port forwarding, firewall changes at the carrier boundary, VPN setup, or a public IP address. It does not remove CGNAT. It creates a separate path around the inbound limitation.
Gateway models, firmware, plans, and network deployments can change. Review the current gateway controls and official T-Mobile Home Internet support information for your service. A menu shown on one gateway model or an older tutorial does not establish that the same option exists or provides public reachability on every current connection.
What CGNAT changes in the network path
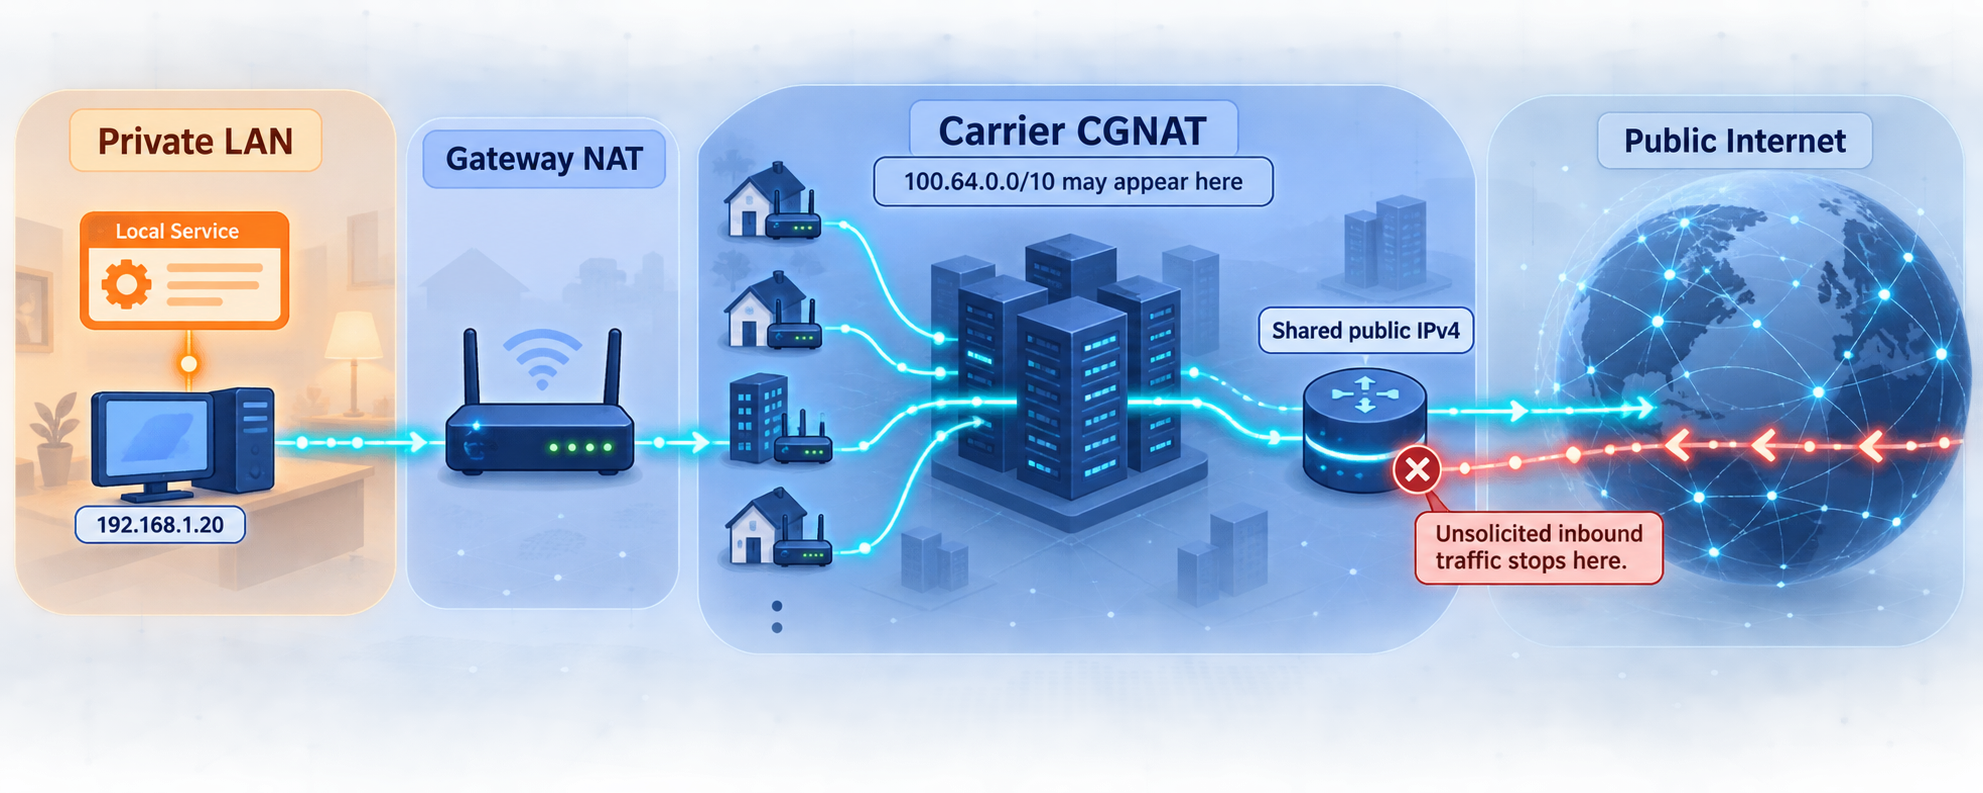
Network Address Translation allows devices using internal addresses to communicate through another address. In a conventional home IPv4 arrangement, computers and phones receive private LAN addresses from the router. The router translates their outbound connections to an IPv4 address assigned by the internet provider.
If the router receives a publicly reachable IPv4 address, it may be possible to configure a port-forwarding rule. For example, the router could direct an incoming TCP connection on a selected public port to a web server on a fixed LAN address. The rule works because the public packet reaches a device you control before it needs to be translated to the internal destination.
CGNAT adds another translation layer inside the provider network. Your gateway receives an address that is not itself the final public IPv4 address used on the internet. The carrier translates traffic again, allowing multiple subscribers to share public IPv4 addresses. Outbound connections can be tracked because a device inside the network initiated them. An unsolicited inbound connection has no subscriber-specific mapping unless the carrier provides one.
The shared IPv4 block 100.64.0.0/10, covering 100.64.0.0 through 100.127.255.255, was reserved for service-provider shared address space by RFC 6598. It is not ordinary globally routable public address space, and it is distinct from the private address ranges commonly used on home LANs.
The resulting path can contain two translation boundaries:
- Your home gateway translates between the LAN and its provider-facing address.
- The provider translates between subscriber-facing shared addressing and a public IPv4 address.
A forwarding rule on the first device cannot configure the second device. That is why a gateway may accept and display a local port-forwarding rule even though outside traffic never reaches it.
How to diagnose CGNAT accurately
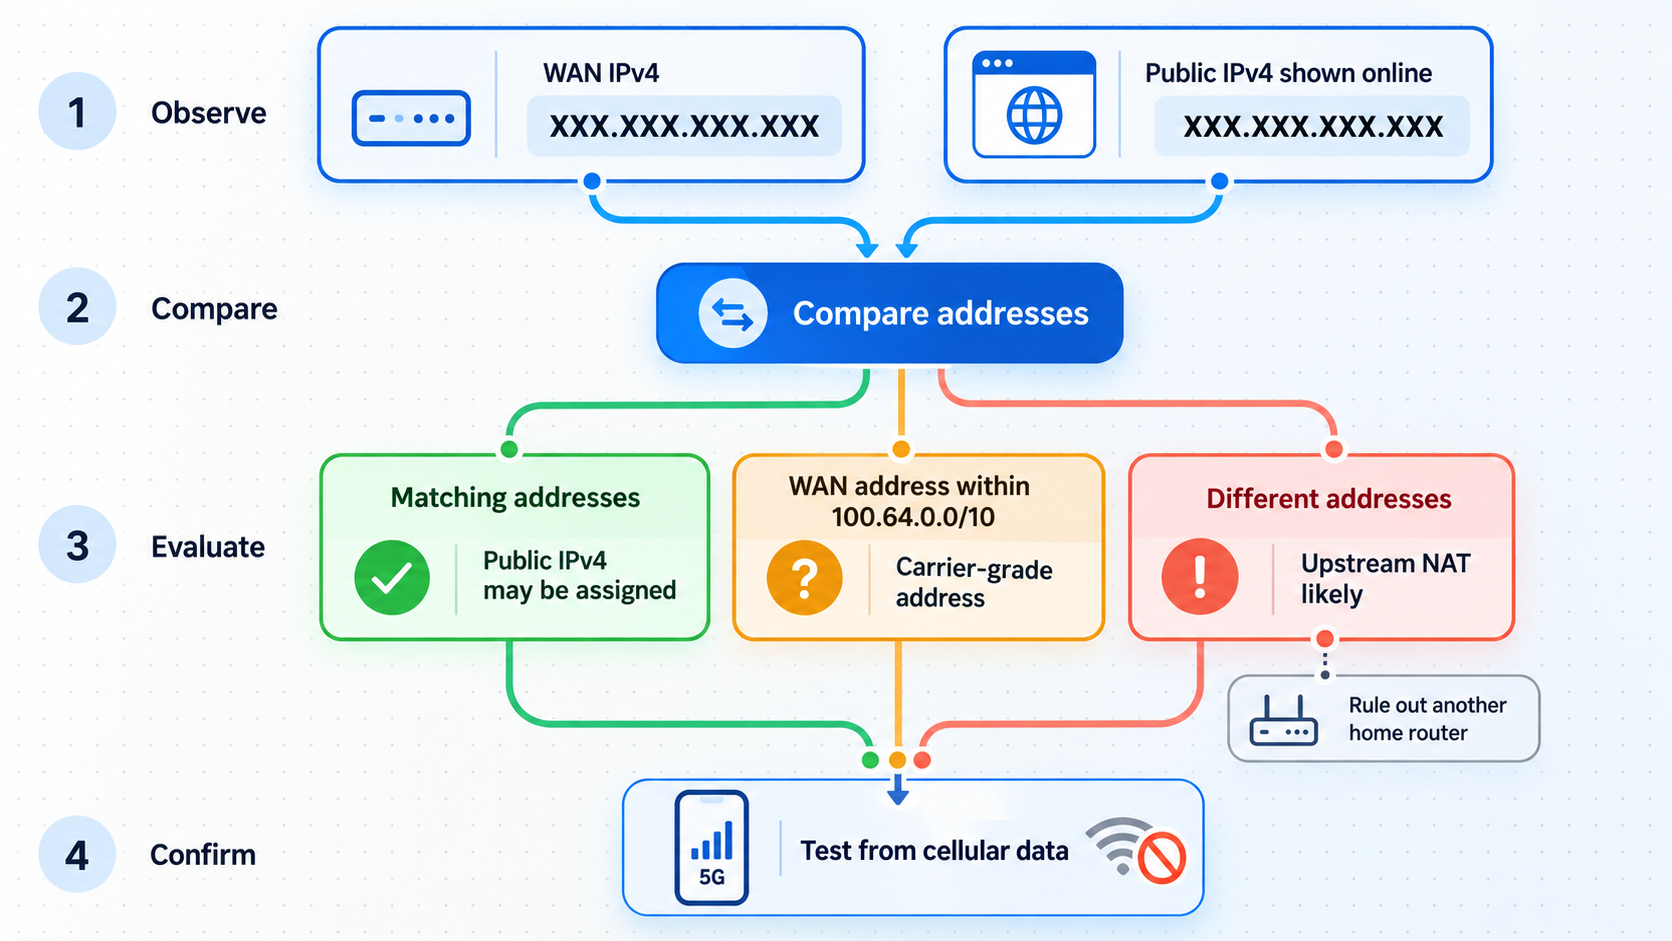
A WAN-versus-public-address comparison is a useful diagnostic, but it must be interpreted carefully. It is evidence about the address path, not an absolute proof of every provider implementation.
Find the gateway's provider-facing IPv4 address
Open the T-Mobile gateway interface or app and locate the internet, WAN, or provider-facing IPv4 status if the current model exposes it. Do not confuse this with the gateway's LAN address, such as an address used by your browser to open its administration interface.
Observe the public IPv4 address used by an outbound request
From a device connected through the same home internet service, use a reputable public IP-checking service. Record only the address needed for comparison. Do not publish screenshots containing gateway passwords, serial numbers, account data, device tokens, or other identifiers.
Compare the addresses and classify the result
A gateway WAN address in 100.64.0.0/10 is a strong CGNAT indicator. A private WAN address from 10.0.0.0/8, 172.16.0.0/12, or 192.168.0.0/16 also shows that another IPv4 routing or translation boundary exists upstream. A different public address on the internet-facing test likewise indicates that the gateway is not directly using the observed public address.
Understand what a matching result does not prove
Matching addresses make a directly assigned public IPv4 path more plausible, but they do not prove that inbound traffic is allowed. Gateway firewall rules, provider filtering, application binding, protocol selection, and local firewalls can still block access.
Some gateways do not support NAT loopback, while others handle it differently. A test from the same LAN can therefore fail even when an external path works, or appear to work through local name resolution without proving external reachability. Perform the final test from a genuinely separate network, such as a phone with Wi-Fi disabled or a remote system you control.
Why the comparison has limits
Address mismatches can also arise from a second router installed inside the home, a modem-router combination, a managed security appliance, or another form of upstream translation. Conversely, provider networks can use transition mechanisms or internal routing that are not fully described by one displayed address. The comparison tells you that another boundary probably exists. It does not reveal every implementation detail or guarantee that a particular inbound feature is supported.
If your gateway does not display a meaningful provider-facing IPv4 address, do not guess from the LAN address. Treat the missing value as an inconclusive test and use the provider's current documentation, support channel, and practical external testing to establish what is possible.
Test IPv6 without assuming it solves the problem
IPv6 can provide globally scoped addresses without traditional IPv4 NAT, but a global IPv6 address does not automatically make an application reachable. The host firewall, gateway firewall, provider policy, application bind address, prefix stability, and the remote client's IPv6 connectivity all matter.
Use a deliberate dual-stack test:
- On the server, inspect the network interfaces for a global IPv6 address. On Linux,
ip -6 addresscan show configured addresses. Avoid treating link-local addresses beginning withfe80:as internet-routable destinations. - Confirm that the application is listening on IPv6, not only on IPv4 loopback. On Linux,
ss -lntupcan show listening TCP and UDP sockets. - Review the host firewall and current gateway firewall controls. Permit only the required protocol and port if direct IPv6 exposure is intended.
- From a separate network with working IPv6, connect to the service using its IPv6 destination. For an HTTP service on a nonstandard port, IPv6 URL syntax uses brackets, such as
http://[2001:db8::10]:8080/. The documentation prefix in this example must be replaced with the server's real address. - Repeat the test after reconnecting or after enough time has passed to determine whether the address or delegated prefix remains suitable for your use case.
A successful IPv6 test from one location does not guarantee that every visitor, mobile network, workplace, or application can use the same path. Current T-Mobile policy, gateway firewall behavior, and address stability may vary. If dependable access from both IPv4 and IPv6 clients is required, use a method that supplies the appropriate public endpoint rather than assuming direct IPv6 is universal.
Why common router fixes do not remove carrier NAT
Several familiar techniques are useful when the home gateway owns the relevant public address. None can independently create a subscriber-specific inbound mapping at a carrier NAT layer.
These techniques are not inherently defective. They simply solve different problems. Dynamic DNS is useful when a publicly reachable address changes. UPnP can automate mappings on a router that owns the public address. Bridge mode can eliminate local double NAT. Their limitation is that the controlling device must have authority over the relevant inbound boundary.
When inbound connectivity is actually required
Before creating any public endpoint, determine whether the application truly needs one. Cloud-managed products and client applications often keep outbound sessions open to a vendor service. They do not require a stranger on the internet to initiate a connection to your gateway.
A public tunnel can be discovered and attacked like any other internet endpoint. Avoid directly publishing router consoles, cameras, databases, remote desktop services, or unauthenticated IoT panels. Use strong application authentication, current software, least-privilege accounts, access restrictions where available, and a private VPN when access does not need to be public.
Compare alternatives to traditional port forwarding
| Approach | Best suited to | What it requires | Important limitation |
|---|---|---|---|
| Provider-supported public IPv4 | Applications designed for direct inbound connectivity | A current provider offering and a gateway path that supports the required inbound traffic | Availability, cost, address stability, and supported service types depend on the provider and plan. |
| Direct IPv6 | Applications and clients with end-to-end IPv6 support | A global server address, correct application binding, firewall configuration, and IPv6 on the remote network | It may not work from IPv4-only clients, and address or firewall behavior can vary. |
| Localtonet public tunnel | Publishing a selected HTTP, TCP, UDP, combined UDP/TCP, TLS, or File Server target | A connected Localtonet client and a running tunnel of the correct type | The endpoint depends on the local client, local service, home connection, and tunnel remaining available. |
| Localtonet VPN Manager | Private access between authorized devices or LANs | VPN membership and configuration on participating systems | It is private mesh VPN access, not a public endpoint for arbitrary internet visitors. |
| Self-managed VPS relay | Teams that want to operate and control their own public relay | A public server, tunnel software, firewall policy, authentication, updates, monitoring, and incident response | You assume the security and operational work for the internet-facing server. |
| External application hosting | Persistent public services that should not depend on a home connection | Deployment and storage outside the home network | Migration, hosting resources, maintenance, and data handling must be planned. |
A public tunnel and a private VPN answer different questions. Use a tunnel when an external service or member of the public needs a reachable endpoint. Use VPN Manager when only enrolled devices or connected private networks should have access. Standard Localtonet HTTP, TCP, UDP, TLS, and File Server tunnels should not be described as VPN functionality.
Prerequisites before creating a Localtonet tunnel
Complete the local service setup before involving CGNAT or Localtonet. A tunnel can carry traffic to a reachable target, but it cannot repair an application that is stopped, listening on the wrong interface, blocked by the host firewall, or configured for another protocol.
- A Localtonet account and a device-specific authentication token.
- A supported Localtonet client environment. Current documented choices include Windows 64-bit, 32-bit, ARM, and ARM64 builds; Linux 64-bit, ARM, ARM64, and MUSL variants; macOS 64-bit and ARM64; Docker; Android; installable Linux DEB and RPM packages; Termux on ARM64 Android; and experimental x64 or ARM64 OpenWrt packages for listed firmware generations.
- A computer or device that will stay powered on and can reach the target service or folder.
- The target's local IP address, port, and transport protocol, or the local folder path for File Server.
- Application-level authentication and authorization suitable for remote access.
- An external test network that is separate from the T-Mobile Home Internet connection.
Package requirements vary. The current Linux DEB and RPM packages require systemd 247 or newer and OpenSSL 3, with documented examples including Debian 12, Ubuntu 22.04 or newer, and RHEL 9. OpenWrt packages are experimental, architecture-specific, and limited to the currently listed firmware and CPU combinations. Check the current Localtonet download and installation documentation before choosing a build.
Verify the application locally first
Test from the same device whenever possible. Then, if the Localtonet client will run on another LAN device, repeat the test from that client device. This second test catches bind-address and local firewall problems before they are mistaken for tunnel failures.
For an HTTP application on port 8080:
curl -i http://127.0.0.1:8080/An HTTP response such as 200, 301, 302, 401, or 403 proves that an HTTP server answered. An authentication response can be expected and is different from a connection refusal or timeout.
For a TCP service, use the service's native client when available. A basic connection test from another machine can also establish whether a TCP listener accepts connections:
nc -vz 192.168.1.50 25565Replace the example LAN address and port with the actual target. A successful TCP connection does not prove that the application's full protocol exchange works, so complete a native-client login or request as well.
UDP has no TCP-style connection handshake. A generic port probe can therefore be inconclusive. Use the application's native client and confirm an application-level response, server log entry, or known request and response exchange. Also verify that the server is configured for UDP rather than assuming that a TCP listener on the same port is sufficient.
Choose the correct Localtonet tunnel family
Select the tunnel according to what the local application actually speaks. Availability of a particular option, relay, region, or capability can vary by plan, client version, or deployment, so confirm current choices in the dashboard.
| Tunnel or access type | Use it for | Local target | Key check |
|---|---|---|---|
| HTTP/s | Websites, APIs, dashboards, and webhook receivers | Local IP address and web application port | Confirm the application accepts the forwarded host and reverse-proxy context. |
| TCP | Applications that use a raw TCP connection | Local IP address and TCP port | Verify that the service is listening on TCP and test with its native client. |
| UDP | Applications that use UDP datagrams | Local IP address and UDP port | Verify with an application-level response because UDP has no connection handshake. |
| Combined UDP/TCP | Software that requires both transports | Local IP address and the applicable port target | Confirm that the application genuinely needs both. Do not choose it solely because the protocol is unknown. |
| TLS | A local service whose expected tunnel type is TLS | Local IP address and port | Confirm current product options and the application's TLS behavior before deployment. |
| File Server | Publishing and managing a local folder | A local folder path | Do not enter an IP address and port as though it were a normal service tunnel. |
| VPN Manager | Private mesh access and bridging authorized private networks | VPN membership and network configuration | Use this for private access, not as a public URL or public port. |
Proxy Server is another Localtonet family, but its purpose is different. HTTP and SOCKS5 proxy tunnels make the connected device the proxy exit node. They do not forward public traffic to a conventional local IP address and port, so they are not the normal choice for publishing a home server.
Game compatibility must be evaluated separately. A game may rely on TCP, UDP, both transports, peer discovery, platform matchmaking, source-port behavior, or proprietary NAT traversal. Creating a reachable port does not guarantee an “open NAT” classification, lower latency, console compatibility, or successful matchmaking.
Install and run the Localtonet client
Download the appropriate client from the Localtonet documentation. Windows, macOS, Docker, Android, Linux archive, Linux package, Termux, and experimental OpenWrt paths are currently documented. Follow the instructions shown for the exact operating system and architecture rather than substituting a binary intended for another platform.
Exact Debian or Ubuntu x64 package workflow
The following three-step sequence matches the current documented x64 DEB package workflow. It requires systemd 247 or newer and OpenSSL 3.
Install the downloaded package
Open a terminal in the directory containing localtonet-linux-x64.deb, then install that local package.
sudo apt install ./localtonet-linux-x64.debStore and validate the device AuthToken
Edit /etc/localtonet/auth-token as root and replace the dummy value with the device-specific token on one line. Restrict the file, then validate the configuration. Do not paste the token into a public terminal transcript.
sudo chmod 600 /etc/localtonet/auth-token
sudo localtonet --headless --authtoken-file /etc/localtonet/auth-token --check-configEnable and start the service
After the configuration check succeeds, enable the Localtonet service and review its journal.
sudo systemctl enable --now localtonet.service
sudo journalctl -u localtonet.service
The ARM64 Debian and Ubuntu package follows the same three actions with the documented ARM64 package filename. RPM packages are available for the documented Fedora and RHEL x64 and ARM64 environments and use the corresponding dnf install command. For upgrades, install the new package and restart localtonet.service; the package workflow preserves the configuration.
The token identifies the client device that can run tunnels. Treat it as a credential. Do not include it in screenshots, shell history shared with others, public repositories, support posts, or application logs.
Configure the appropriate public or private access path
Network service lifecycle for HTTP, TCP, UDP, combined UDP/TCP, or TLS
For a network service, first select the corresponding tunnel family in the current dashboard. Select the authenticated device that can reach the local target and choose a relay server or region from the values currently offered. Do not copy a server code from an old tutorial because available values can change.
Enter the local target IP address and port. If the application runs on the same machine as the client and listens on loopback, its target may be a loopback address. If it runs on another LAN device, enter that device's stable LAN address and ensure the client machine can already reach it. Choose the applicable process or public-address option where the selected tunnel family presents one.
Create the tunnel, then explicitly press Start. Creation and startup are separate lifecycle actions. The public endpoint becomes usable only while the selected client is connected and the tunnel is running.
The exact fields differ between tunnel families. Use the protocol-specific page reached through the current documentation navigation for field names and options shown by the current product. This guide does not combine those different forms into an artificial universal sequence.
Exact File Server setup workflow
File Server is different because it publishes a local folder rather than forwarding to a listening IP address and port. The documented setup sequence is:
Install the Localtonet app for the operating system
Install and run the appropriate Localtonet client on the device that can read the folder.
Open the File Server Tunnel page
Use the File Server section rather than creating an HTTP, TCP, or UDP target.
Select the Process Type
Choose Random Sub Domain, Custom Sub Domain, or Custom Domain according to the currently available configuration. These process types serve the File Server content at a public HTTPS address.
Select the AuthToken and server, then enter the folder path
Choose the connected device and an available server. Enter a local path such as C:\Users\Work on Windows or /root or /usr/share on Linux or macOS.
Press Start
Start the File Server tunnel and use the assigned public address. Review authentication, permissions, and sharing settings before distributing that address.
Current File Server sub-types include Default, SFTP, and WebDAV. Default provides a browser-based file manager, SFTP supports standard SFTP clients and automation, and WebDAV can mount the folder as an operating-system network drive. Features documented for the Default web manager should not automatically be assumed to apply to SFTP or WebDAV unless current product documentation says so.
Use VPN Manager for private access
If the destination should be reachable only by your authorized devices or connected private networks, configure VPN Manager rather than publishing a public service tunnel. VPN Manager provides a private mesh VPN with granular firewall rules and can bridge local LANs. It is separate from standard HTTP, TCP, UDP, TLS, and File Server tunneling.
Verify HTTP, TCP, and UDP access remotely
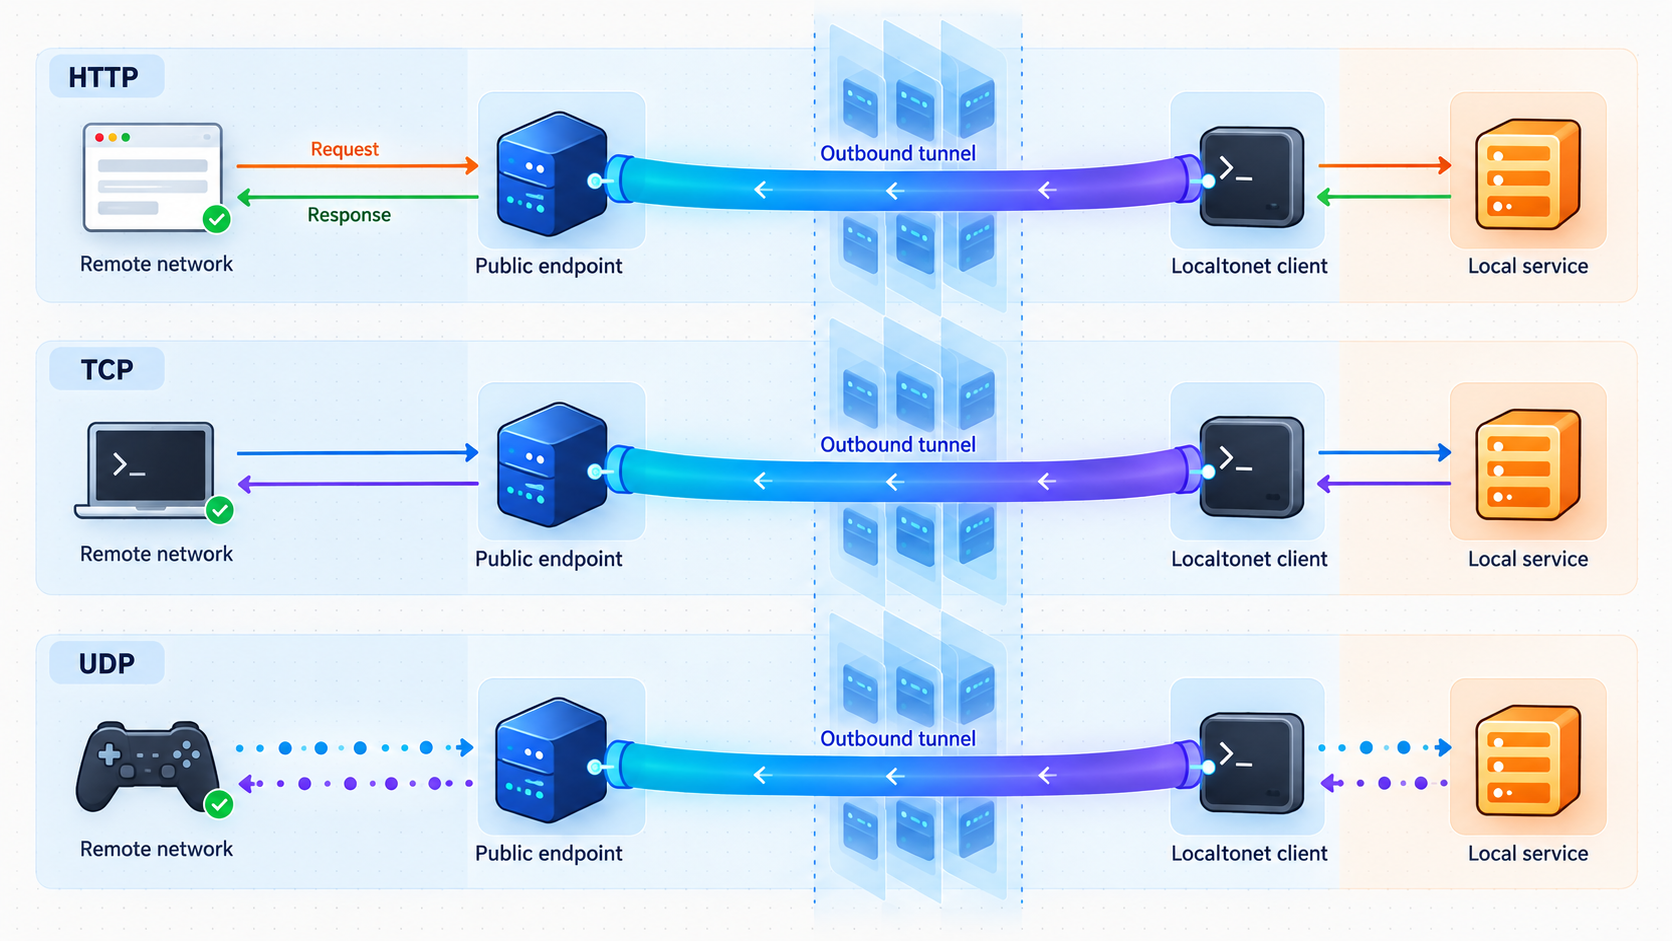
Use a network outside the T-Mobile Home Internet connection. Disable Wi-Fi on a phone before using mobile data, or test from a remote system you control. Confirm that the public hostname and port are the exact values assigned to the running tunnel.
Verify an HTTP or HTTPS application
- Open the assigned public URL in a browser from the external network.
- Use
curlto inspect the response status and headers if the browser shows an ambiguous error. - Complete an application-level action, such as signing in with a test account or sending a non-destructive API request.
- Inspect the local application log to confirm that the request reached the intended process.
curl -i https://your-assigned-public-host/Replace the example with the endpoint assigned by Localtonet. A 401 Unauthorized or 403 Forbidden response may prove that routing works while application authorization is denying the request. Do not mistake an expected authentication response for a tunnel failure.
Verify a TCP service
- Use the assigned public host and public port, not the private LAN address.
- Test whether a TCP connection can be established.
- Use the application's native client to complete its actual handshake, login, or request.
- Check both Localtonet client status and local application logs while testing.
nc -vz your-assigned-public-host 12345A successful generic connection proves only that the TCP path accepted a connection. It does not validate credentials, protocol negotiation, application permissions, or compatibility.
Verify a UDP service
UDP verification must be application-specific. A lack of response to an arbitrary datagram does not establish that the port is closed, because many UDP applications ignore unknown payloads. Use the real client or a documented protocol request, then verify one or more of the following:
- The client receives a valid application response.
- The server records the request in its logs.
- The application reports a successful session or registration.
- A packet capture on the local host shows the expected request reaching the service.
If software requires both TCP and UDP, verify each transport separately. A successful TCP test says nothing about the UDP path on the same numeric port.
Routine operation and outage expectations
A tunnel is not permanently available merely because its configuration exists in the dashboard. Four components must remain healthy: the local application, the device running the Localtonet client, the device's internet connection, and the running tunnel.
- Confirm that the Localtonet client starts after an intended reboot. The documented Linux package can run as a systemd service.
- Keep the target application's address and port stable. Use an appropriate LAN address strategy if the target runs on another device.
- Review application and client logs after updates or network changes.
- Test the public endpoint after changing the application, firewall, operating system, gateway, or tunnel configuration.
- Stop the tunnel when public access is no longer needed. Delete obsolete configurations that should not be started again.
- Restart the documented Localtonet service after a Linux package upgrade.
A local power outage, application crash, client shutdown, home internet interruption, or stopped tunnel can make the endpoint unavailable. Localtonet does not make the home service independent of the device or connection hosting it. If the workload needs availability that should not depend on a residential connection, consider external hosting or another architecture designed for that requirement.
Do not publish assumed uptime, performance, latency, or geographic coverage. Relay and region choices must be taken from the current product, and availability may vary by plan or deployment.
Secure the service before publishing it
CGNAT may have prevented unsolicited IPv4 traffic from reaching the service, but it should not be treated as an application security control. Once a public endpoint exists, the application needs deliberate protection.
- Require application authentication. A secret URL is not a substitute for a login or signed request.
- Use unique credentials and multi-factor authentication where the application supports it.
- Grant the smallest permissions required for remote users or integrations.
- Update the application, operating system, runtime, and dependencies before exposure.
- Restrict access by application policy or available tunnel controls where appropriate.
- Protect device AuthTokens, API credentials, webhook secrets, and private endpoint details.
- Do not expose a database port, router administration page, or remote desktop listener directly when a safer authenticated application layer or private VPN is available.
- Monitor application logs for failed authentication and unexpected requests.
- Stop or delete the tunnel when the task is complete.
HTTP applications also need correct reverse-proxy awareness. Some applications reject an unfamiliar Host header, generate redirects to a private hostname, require an explicit list of trusted proxy addresses, or need configuration before accepting forwarded scheme and client-address information. Follow the application's own reverse-proxy documentation. Do not broadly trust forwarded headers from arbitrary network peers.
Troubleshooting a Localtonet endpoint behind T-Mobile Home Internet
The service is unreachable even on the local machine
Stop troubleshooting the tunnel and repair the application first. Confirm that the process is running, identify the actual port, inspect its logs, and use its native client locally. A connection refusal usually means nothing is listening at that address and port. A timeout can indicate a firewall, routing issue, or unresponsive application.
The service works on localhost but not from the Localtonet client device
The application may be bound only to 127.0.0.1 or ::1. Loopback listeners accept connections only from the same host. If the client runs on another LAN machine, configure the application to listen on an appropriate LAN interface and secure it with a narrow firewall rule. Do not bind indiscriminately to every interface without understanding the exposure.
The local target IP address or port is wrong
Verify the target from the machine running the Localtonet client. A stale LAN address is common when the application runs on another device. Confirm that the numeric port belongs to the intended service and that the tunnel does not point to an old development process.
The tunnel protocol does not match the application
An HTTP tunnel is for an HTTP application. It is not a universal wrapper for arbitrary TCP or UDP traffic. Likewise, a TCP tunnel does not carry UDP merely because both services use the same port number. Choose UDP/TCP only when the application requires both transports and verify each path independently.
The Localtonet client is disconnected
Check that the client process or service is running and authenticated with the intended device token. On a documented Linux package installation, inspect the service and journal:
sudo systemctl status localtonet.service
sudo journalctl -u localtonet.service
Also confirm that the device has working outbound internet access. Revalidate the configuration if the token file or installation changed.
The tunnel exists but was never started
Creating a configuration does not start it. Open the dashboard, select the correct device and tunnel, and press Start. Check that the status reflects a connected client and running tunnel before testing the public endpoint.
The local firewall blocks the client-to-service path
A service can work on loopback while a host firewall rejects connections from another LAN device. Add only the rule needed for the Localtonet client device and service port. Avoid disabling the entire firewall as a diagnostic shortcut. If the client runs on the same machine and targets loopback, confirm that local security software is not blocking that process or port.
The public web endpoint returns an application error
An HTTP status response usually means traffic reached an HTTP server. Investigate the application rather than immediately changing the tunnel. Common causes include missing authentication, an untrusted proxy configuration, a rejected host header, an incorrect base URL, redirects to a private hostname, or an application that expects HTTPS information from a trusted reverse proxy.
Compare the public response with the local response, inspect application logs, and follow that application's reverse-proxy guidance. Configure trusted proxies narrowly. Never disable host validation or trust all forwarding headers merely to suppress an error.
The browser works, but a webhook provider fails
Check whether the provider requires a particular method, path, response code, signature, or timeout. Confirm that the public URL includes the full callback path and that application authentication is compatible with automated requests. Review both provider delivery logs and local application logs.
A TCP probe succeeds, but the application client fails
The network path may be open while protocol negotiation fails. Check server version compatibility, TLS expectations, application credentials, source restrictions, and whether the client is connecting to the assigned public port rather than the local service port.
A UDP test gives no clear result
Use the native client and watch the server log or a packet capture. Confirm that the application is listening on UDP, that the Localtonet tunnel is UDP or combined UDP/TCP as required, and that the request format is valid. Generic UDP scans often report ambiguous results because there is no connection handshake.
Testing succeeds only from the home Wi-Fi
You may be reaching a private address, a local DNS override, or a locally routed hostname instead of the public tunnel. Turn off Wi-Fi on the test phone and verify that it is using an independent network. Re-enter the exact assigned public URL or host and port.
Testing fails only from one external network
The remote network may block the destination port, lack IPv6, filter UDP, or enforce an application policy. Test from a second independent network. If one path works and another does not, investigate the remote network rather than changing a working local target.
Frequently asked questions
Does T-Mobile Home Internet support traditional IPv4 port forwarding?
Traditional forwarding cannot create a publicly reachable port when the connection is behind carrier-side NAT because the home gateway does not control the upstream translation. Gateway, firmware, plan, and network behavior can change, so check current official T-Mobile support information for your specific service rather than relying on an older router guide.
Does a 100.64.x.x WAN address prove CGNAT?
An address in 100.64.0.0/10 is a strong indicator because RFC 6598 reserves that block as shared address space for service-provider use. It is not globally routable public IPv4 space. Address comparison should still be combined with current provider information and practical external testing.
Will adding my own router fix T-Mobile CGNAT?
No. Another router can improve local networking or provide different firewall controls, but it cannot create a mapping on a carrier NAT device. It may also add another local NAT layer unless the equipment supports an appropriate bridge or passthrough arrangement.
Will dynamic DNS make a CGNAT connection reachable?
No. Dynamic DNS maps a hostname to an address. It does not create an inbound route or carrier-side port mapping. It is useful when a directly reachable public address changes, but it cannot turn a shared carrier address into a dedicated endpoint.
Does Localtonet remove CGNAT?
No. CGNAT remains in place. The Localtonet client establishes an outbound connection to a relay, and the assigned public endpoint carries traffic back through that connection to the selected local target.
Can Localtonet expose TCP and UDP services?
Localtonet documents TCP, UDP, and combined UDP/TCP tunnel families in addition to HTTP/s, TLS, and File Server. Select the family that matches the application. Availability of individual options may vary by plan, client version, or deployment.
Will a tunnel guarantee that my game reports an open NAT?
No. Games and consoles can use platform-specific matchmaking, peer discovery, multiple ports, both transport protocols, or proprietary NAT traversal. A reachable tunnel endpoint does not guarantee open NAT status, compatibility, or lower latency. Test the actual server and client workflow.
Should I use a public tunnel or VPN Manager?
Use a public tunnel when an external user or service needs a public URL or public host and port. Use VPN Manager when access should remain private to authorized devices or connected networks. VPN Manager is our VPN feature and is distinct from standard tunnels.
Does the endpoint remain available when the local client stops?
No. The selected client must remain connected and the tunnel must be running. A stopped client, stopped tunnel, application failure, local power outage, or home internet interruption can make the endpoint unavailable.
Publish the service you need without changing the carrier NAT
Verify the application locally, choose the matching Localtonet tunnel family, start the tunnel, and test its assigned endpoint from a genuinely external network.
Get Started Free →

